Choosing the right iso agent program can significantly impact your organization’s compliance efforts and operational efficiency. The best overall pick, ISO 27001 Implementation Using AI, offers a balance of automation and speed, ideal for teams aiming to reduce documentation time. Building an ISMS with ISO/IEC 27001:2022 Made Practical stands out for practical guidance suitable for organizations seeking clarity and step-by-step instructions. However, each option involves tradeoffs, such as cost versus depth of features or ease of use versus customization. Continue reading for a detailed breakdown of the top programs, helping you find the best fit for your needs.

Get business pricing on office and shipping supplies
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- The top picks balance automation features with ease of implementation, making compliance more accessible.
- Price and complexity vary widely; more advanced programs tend to require higher investment and expertise.
- Practical guides and handbooks are best for organizations new to ISO standards, while advanced tools suit experienced teams.
- Customized solutions often come with steeper learning curves but offer more flexibility for complex needs.
- Automation and AI integration are emerging as key differentiators among leading iso agent programs.
| ISO 27001 Implementation Using AI: Reduce Documentation Effort and Accelerate Certification |  | Best for AI-Driven ISO 27001 Implementation | Focus Area: AI-assisted ISO 27001 implementation | Intended Audience: Organizations with AI integration experience | Content Depth: Practical strategies, limited technical details | VIEW ON AMAZON | See Our Full Breakdown |
| Building an ISMS with ISO/IEC 27001:2022 Made Practical |  | Best for Step-by-Step Implementation and Continuous Improvement | Approach: Step-by-step implementation | Focus: Continuous improvement | Intended Audience: Security practitioners and managers | VIEW ON AMAZON | See Our Full Breakdown |
| Leading and Mastering ISO 27001:2022: A Practical Guide to Building a High-Performing Information Security Management System |  | Best for Strategic Security Leadership | Coverage: High-level management strategies | Focus Area: Building high-performance ISMS | Target Audience: Security executives and strategic planners | VIEW ON AMAZON | See Our Full Breakdown |
| ISO 27001 ISMS Handbook: Implementing and Auditing an Information Security Management System in Small and Medium-Sized Businesses |  | Best for SMBs Seeking Practical Implementation and Auditing Tips | Target Audience: SMBs and mid-sized organizations | Content Focus: Implementation and auditing | Technical Detail: Basic, practical guidance | VIEW ON AMAZON | See Our Full Breakdown |
| ISO 9000 Quality Systems Handbook – Updated for ISO 9001:2015 Standard |  | Best for Quality Management System Upgrades | Focus: Quality management systems | Standards: ISO 9001:2015 | Content Type: Procedural and strategic guidance | VIEW ON AMAZON | See Our Full Breakdown |
| ISO 9001:2026 Transition Guide for U.S. Organizations |  | Best for Transition Planning and In-Depth Clause Comparison | Content Focus: ISO 9001:2026 transition | Format: Clause-by-clause comparison, templates, self-assessment | Intended Audience: Organizations updating from ISO 9001:2015 | VIEW ON AMAZON | See Our Full Breakdown |
| The Complete ISO 27001 Handbook: From Basics to Advanced | 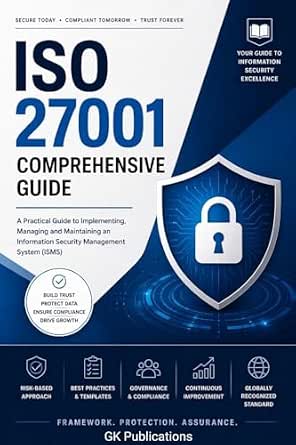 | Best for Comprehensive ISO 27001 Application | Coverage: ISO 27001 standards and controls | Intended Audience: Beginners to advanced users | Application Focus: Implementation and certification | VIEW ON AMAZON | See Our Full Breakdown |
| ISO/IEC 27001:2022 Lead Auditor Examination Guide: 500 Practice Questions with Explanations, Audit Scenarios & Tips |  | Best for Exam Preparation and Audit Scenario Practice | Number of Practice Questions: 500 | Content Types: Questions, explanations, scenarios, tips | Focus: Exam readiness | VIEW ON AMAZON | See Our Full Breakdown |
| The Ultimate ISO 9001:2015 Audit Checklist: Navigate the ISO 9001:2015 Audit Process with Confidence |  | Best for Step-by-Step Audit Preparation | Content Focus: Audit process navigation | Format: Step-by-step checklist | Intended Audience: Organizations preparing for ISO 9001:2015 audits | VIEW ON AMAZON | See Our Full Breakdown |
| ISO 9001:2026 – What Changed, What Your Auditor Will Look For, and How to Close the Gaps |  | Best for Understanding ISO 9001:2026 Updates and Gap Closure | Content Focus: ISO 9001:2026 updates and gap analysis | Format: Guided strategies and explanations | Intended Audience: Organizations preparing for ISO 9001:2026 audits | VIEW ON AMAZON | See Our Full Breakdown |
| iso agent program | Intended Audience | Technical Detail |
|---|---|---|
| ISO 27001 Implementation Using | Organizations with AI integration experience | — |
| Building an ISMS with ISO/IEC | Security practitioners and managers | Moderate, implementation-focused |
| Leading and Mastering ISO 2700 | — | — |
| ISO 27001 ISMS Handbook: Imple | — | Basic, practical guidance |
| ISO 9000 Quality Systems Handb | — | Broad, process-oriented |
| ISO 9001:2026 Transition Guide | Organizations updating from ISO 9001:2015 | — |
| The Complete ISO 27001 Handboo | Beginners to advanced users | General guidance, no deep technical specs |
| ISO/IEC 27001:2022 Lead Audito | Aspiring ISO 27001 lead auditors | Practice questions, no technical content |
| The Ultimate ISO 9001:2015 Aud | Organizations preparing for ISO 9001:2015 audits | — |
| ISO 9001:2026 | Organizations preparing for ISO 9001:2026 audits | — |
More Details on Our Top Picks
ISO 27001 Implementation Using AI: Reduce Documentation Effort and Accelerate Certification
This book stands out for organizations seeking to leverage AI tools to streamline ISO 27001 compliance. Compared with traditional guides like Building an ISMS with ISO/IEC 27001:2022, it focuses on automating documentation tasks, which can significantly cut down certification time. However, it offers less detailed technical content, making it less suitable for those unfamiliar with AI or ISO standards. Its practical strategies are ideal for teams aiming to speed up processes without deep technical dive, but organizations needing comprehensive technical procedures might find it lacking.
Pros:- Helps reduce documentation effort significantly
- Speeds up ISO 27001 certification process
- Provides practical, easy-to-apply strategies
Cons:- Lacks detailed technical content
- Requires prior knowledge of ISO 27001 and AI tools
Best for: Organizations looking to incorporate AI tools to simplify ISO 27001 documentation and accelerate certification.
Not ideal for: Large enterprises requiring in-depth technical implementation guidance or detailed auditing procedures.
- Focus Area:AI-assisted ISO 27001 implementation
- Intended Audience:Organizations with AI integration experience
- Content Depth:Practical strategies, limited technical details
- Certification Speed Focus:Yes
- Documentation Reduction:Significant
- Prerequisites:Basic ISO 27001 and AI knowledge
Our verdict“Best suited for organizations aiming to leverage AI for faster ISO 27001 compliance with minimal technical complexity.”
Building an ISMS with ISO/IEC 27001:2022 Made Practical
This pick makes the most sense for security professionals seeking a structured, actionable guide to building and maintaining an ISO 27001:2022 compliant ISMS. Unlike Leading and Mastering ISO 27001:2022, which offers broader management strategies, this book emphasizes a clear, step-by-step approach and ongoing improvement. Its focus on practical implementation makes it ideal for teams new to ISO 27001 but may challenge those looking for more strategic or high-level guidance. It’s especially suitable for organizations committed to continuous security enhancement.
Pros:- Clear, step-by-step implementation guidance
- Focus on continuous improvement
- Part of a reputable security series
Cons:- No pricing or customer ratings available
- Content may be too technical for complete beginners
Best for: Security teams or managers implementing ISO/IEC 27001:2022 for the first time or seeking a practical, progressive approach.
Not ideal for: Organizations requiring in-depth technical audits or comprehensive technical specifications without step-by-step guidance.
- Approach:Step-by-step implementation
- Focus:Continuous improvement
- Intended Audience:Security practitioners and managers
- Series:Security Implementation Series
- Technical Detail:Moderate, implementation-focused
- Applicability:Practical for teams new to ISO 27001
Our verdict“Ideal for security professionals who need a practical, structured approach to building and improving their ISO 27001:2022 ISMS.”
Leading and Mastering ISO 27001:2022: A Practical Guide to Building a High-Performing Information Security Management System
This comprehensive guide is better suited for organizations seeking a broad understanding of ISO 27001:2022 standards and strategies to elevate their security management systems. Unlike Building an ISMS with ISO/IEC 27001:2022, which emphasizes implementation steps, this book covers high-level management and leadership strategies, making it more technical and strategic. It lacks specific tools or detailed step-by-step procedures but offers valuable insights for security leaders aiming to foster a high-performing security environment. It’s less appropriate for teams seeking hands-on technical guidance.
Pros:- Comprehensive coverage of ISO 27001:2022 standards
- Focus on building high-performing security systems
- Practical guidance for management strategies
Cons:- Lacks specific implementation tools
- May be too technical or strategic for beginners
Best for: Security leaders and senior managers aiming to develop strategic, high-impact information security systems.
Not ideal for: Operational teams or implementers looking for detailed, step-by-step procedures or technical checklists.
- Coverage:High-level management strategies
- Focus Area:Building high-performance ISMS
- Target Audience:Security executives and strategic planners
- Technical Content:Strategic, less technical details
- Application:Leadership and organizational development
- Approach:Guidance on management practices
Our verdict“Best for organizational leaders seeking to develop strategic, high-level security management practices aligned with ISO 27001:2022.”
ISO 27001 ISMS Handbook: Implementing and Auditing an Information Security Management System in Small and Medium-Sized Businesses
This handbook is tailored for small and medium-sized businesses aiming to implement and audit ISO 27001. Unlike the more comprehensive books like Building an ISMS with ISO/IEC 27001:2022, it provides focused, practical steps specifically suited for smaller organizations. Its auditing tips help ensure ongoing compliance, but it doesn’t delve into highly technical procedures, making it accessible yet limited for organizations with complex security needs. It’s a strong choice for SMBs wanting straightforward guidance.
Pros:- Practical guidance tailored for SMBs
- Includes auditing tips for ongoing compliance
- Clear steps for establishing and maintaining ISMS
Cons:- No detailed technical procedures
- Requires prior ISO knowledge for best results
Best for: SMBs or mid-sized organizations looking for practical, easy-to-follow ISO 27001 implementation and audit guidance.
Not ideal for: Large enterprises or organizations requiring detailed technical procedures and complex security architectures.
- Target Audience:SMBs and mid-sized organizations
- Content Focus:Implementation and auditing
- Technical Detail:Basic, practical guidance
- Applicability:Small to medium organizations
- Audit Tips:Included
- Prerequisites:Basic ISO familiarity
Our verdict“Perfect for small and medium-sized organizations seeking straightforward implementation and auditing guidance for ISO 27001.”
ISO 9000 Quality Systems Handbook – Updated for ISO 9001:2015 Standard
This handbook offers a comprehensive approach to implementing ISO 9000/9001:2015 quality management systems, making it ideal for organizations looking to improve their processes systematically. While Building an ISMS focuses specifically on security, this resource covers broader quality principles and process improvements. It’s better suited for organizations aiming for overall process quality rather than ISO 27001-specific security controls. The lack of detailed technical procedures means it’s more strategic and procedural in nature.
Pros:- Updated guidance for ISO 9001:2015
- Comprehensive resource for quality management
- Helps improve organizational processes
Cons:- No specific features or editions mentioned
- Lacks detailed technical procedures for security
Best for: Organizations seeking to upgrade their quality management systems in line with ISO 9001:2015 standards.
Not ideal for: Organizations primarily focused on information security management or needing detailed security controls guidance.
- Focus:Quality management systems
- Standards:ISO 9001:2015
- Content Type:Procedural and strategic guidance
- Target Audience:Quality managers and process improvement teams
- Technical Detail:Broad, process-oriented
- Application:Organizational quality enhancement
Our verdict“Ideal for organizations aiming to enhance overall quality systems under ISO 9001:2015, not specific to security or ISO 27001.”
ISO 9001:2026 Transition Guide for U.S. Organizations
This guide stands out for organizations needing a structured approach to transitioning from ISO 9001:2015 to 9001:2026. It provides detailed clause-by-clause comparisons that clarify what changes are essential, making it ideal for companies with existing ISO 9001 systems. Compared to the more general Ultimate ISO 9001:2015 Audit Checklist, this resource offers deeper insights into compliance requirements, though it can be overwhelming for beginners due to its complexity. The included templates and self-assessment tools streamline the transition process, but the lack of pricing info and the technical nature may deter smaller organizations or those new to ISO standards.
Pros:- Provides a comprehensive clause-by-clause comparison for clarity on changes
- Includes practical templates to facilitate implementation
- Offers a self-assessment tool to gauge readiness and compliance
Cons:- Content can be complex and intimidating for beginners
- No specific pricing information available, which may hinder budget planning
Best for: Mid-sized to large organizations actively updating their quality management systems to ISO 9001:2026.
Not ideal for: Small businesses or newcomers to ISO standards, as the content may be too technical and complex.
- Content Focus:ISO 9001:2026 transition
- Format:Clause-by-clause comparison, templates, self-assessment
- Intended Audience:Organizations updating from ISO 9001:2015
- Complexity:Advanced
- Support Tools:Templates, self-assessment
Our verdict“This guide is ideal for organizations seeking a detailed, structured approach to ISO 9001:2026 transition, especially those with existing ISO experience.”
The Complete ISO 27001 Handbook: From Basics to Advanced
This handbook makes the list for its thorough coverage of ISO 27001 standards and practical guidance, suitable for both beginners and seasoned professionals. It compares favorably with the ISO/IEC 27001:2022 Lead Auditor Examination Guide by providing foundational knowledge alongside advanced strategies for implementing ISMS and achieving certification. The lack of detailed technical specifics or publication date may leave some users wanting more granular guidance. Overall, this resource bridges the gap between understanding and applying ISO 27001 effectively, though it demands some prior knowledge for full benefit.
Pros:- Provides a complete overview of ISO 27001 standards and controls
- Suitable for both beginners and experienced users
- Includes practical guidance on achieving certification
Cons:- Lacks detailed technical specifications for advanced implementation
- No information on edition or publication date may affect relevance
Best for: Organizations new to ISO 27001 or those seeking a comprehensive, step-by-step implementation guide.
Not ideal for: Experts looking for technical deep-dives or specific audit tools, as this focuses more on broad coverage than detailed technical specs.
- Coverage:ISO 27001 standards and controls
- Intended Audience:Beginners to advanced users
- Application Focus:Implementation and certification
- Technical Detail:General guidance, no deep technical specs
- Support Material:Practical guidance
- Publication Info:Not specified
Our verdict“This handbook is a strong choice for organizations aiming for a broad understanding and practical application of ISO 27001, especially those starting out or expanding their ISMS.”
ISO/IEC 27001:2022 Lead Auditor Examination Guide: 500 Practice Questions with Explanations, Audit Scenarios & Tips
This guide is invaluable for those preparing for the ISO/IEC 27001:2022 lead auditor exam, offering a massive set of 500 practice questions, detailed explanations, and exam tips. It compares favorably with the The Complete ISO 27001 Handbook by focusing specifically on exam readiness and audit scenarios. The absence of raw content descriptions or technical background limits its use for those without prior ISO knowledge, but for dedicated candidates, it provides extensive practice and understanding. The detailed explanations help clarify complex audit concepts, making it a targeted resource for certification success.
Pros:- Extensive set of 500 practice questions for thorough preparation
- Detailed explanations clarify complex audit topics
- Includes real audit scenarios and useful exam tips
Cons:- Requires prior knowledge of ISO 27001 concepts for maximum benefit
- No raw content or technical details beyond practice questions
Best for: ISO 27001 aspirants and auditors seeking intensive exam practice and scenario-based training.
Not ideal for: Beginners or those looking for general ISO 27001 guidance, as this is highly focused on exam prep rather than implementation.
- Number of Practice Questions:500
- Content Types:Questions, explanations, scenarios, tips
- Focus:Exam readiness
- Intended Audience:Aspiring ISO 27001 lead auditors
- Technical Detail:Practice questions, no technical content
- Support Material:Explanations and audit scenarios
Our verdict“This guide excels for ISO 27001 exam candidates committed to intensive practice and scenario-based learning, but less suitable for beginners or implementation-focused users.”
This checklist earns its spot by offering a comprehensive, step-by-step approach to preparing for ISO 9001:2015 audits, making it ideal for organizations seeking to boost confidence during certification. Unlike the ISO 9001:2026 Transition Guide, which focuses on transition specifics, this checklist emphasizes practical audit navigation, making it suitable for organizations new to ISO 9001 audits. Its simplicity and structured format help ensure nothing is overlooked, but the lack of detailed features or updates may limit its usefulness for complex or evolving systems. The absence of customer reviews also suggests a need for cautious consideration.
Pros:- Provides a detailed, step-by-step audit process
- Helps organizations ensure ISO 9001:2015 compliance
- Boosts confidence during audit execution
Cons:- Lacks specific product features or recent updates
- No customer reviews available for validation
Best for: Organizations preparing for initial or periodic ISO 9001:2015 audits seeking a clear, structured process.
Not ideal for: Organizations requiring the latest updates or detailed technical guidance, as this focuses on audit process navigation.
- Content Focus:Audit process navigation
- Format:Step-by-step checklist
- Intended Audience:Organizations preparing for ISO 9001:2015 audits
- Update Status:Not specified
- Support Material:Audit steps
Our verdict“This checklist is well-suited for organizations seeking a straightforward, guided approach to ISO 9001:2015 audits, especially those new to the process.”
ISO 9001:2026 – What Changed, What Your Auditor Will Look For, and How to Close the Gaps
This guide makes the list by clearly outlining the key updates in ISO 9001:2026 and explaining what auditors will focus on, helping organizations prepare effectively. Compared to the ISO 9001:2015 Audit Checklist, it emphasizes understanding the new requirements and strategic gap closure. It is particularly useful for organizations that need clarity on recent changes but may be less helpful for those seeking detailed technical implementation or process guidance. The focus on audit readiness makes it ideal for organizations prioritizing compliance gaps over operational details.
Pros:- Provides a clear overview of ISO 9001:2026 updates
- Helps identify and close compliance gaps
- Prepares organizations for upcoming audits
Cons:- No detailed technical specifications included
- Content may be too focused on audit readiness for operational teams
Best for: Organizations wanting a clear overview of ISO 9001:2026 changes and strategies to address gaps before audits.
Not ideal for: Organizations looking for in-depth technical implementation plans, as this focuses mainly on audit preparation and compliance gaps.
- Content Focus:ISO 9001:2026 updates and gap analysis
- Format:Guided strategies and explanations
- Intended Audience:Organizations preparing for ISO 9001:2026 audits
- Update Focus:Key changes and auditor focus
- Support Material:Gap closure strategies
Our verdict“This guide is best suited for organizations seeking clarity on ISO 9001:2026 changes and practical strategies to prepare for audits, especially those in transition phases.”
How We Picked
This roundup evaluates iso agent programs based on usability, feature set, scalability, support resources, and overall value. We prioritized tools that streamline compliance processes, reduce manual effort, and integrate automation or AI capabilities. Programs were also assessed on their clarity of instructions, suitability for different organization sizes, and flexibility. Our ranking reflects a balance between ease of adoption for beginners and advanced features for seasoned professionals, ensuring options for various needs and budgets.| iso agent program | Technical Detail |
|---|---|
| ISO 27001 Implementation Using | — |
| Building an ISMS with ISO/IEC | Moderate, implementation-focused |
| Leading and Mastering ISO 2700 | — |
| ISO 27001 ISMS Handbook: Imple | Basic, practical guidance |
| ISO 9000 Quality Systems Handb | Broad, process-oriented |
| ISO 9001:2026 Transition Guide | — |
| The Complete ISO 27001 Handboo | General guidance, no deep technical specs |
| ISO/IEC 27001:2022 Lead Audito | Practice questions, no technical content |
| The Ultimate ISO 9001:2015 Aud | — |
| ISO 9001:2026 | — |
Factors to Consider When Choosing Iso Agent Program
When selecting an iso agent program, organizations should consider several key factors to ensure they choose a solution that aligns with their compliance goals and operational capacity. Beyond basic features, understanding the broader implications of each choice helps prevent costly mistakes and ensures long-term value. Here are some critical considerations to guide your decision:Automation and AI Capabilities
Automation features can dramatically reduce the time spent on documentation, audits, and reporting. AI-driven tools offer predictive insights and smarter workflows, especially valuable for complex or fast-growing organizations. However, higher automation often comes with increased costs and setup complexity, so weigh these benefits against your team’s technical comfort level and budget.
Ease of Use and Learning Curve
Some programs offer highly detailed guidance and intuitive interfaces, which are ideal for organizations new to ISO standards. Conversely, more feature-rich tools might require significant training or prior experience. Selecting a solution that matches your team’s familiarity with compliance processes helps prevent frustration and accelerates implementation.
Support and Resources
Look for programs that provide comprehensive support, including tutorials, user communities, and dedicated customer service. This support structure can be crucial during initial setup and ongoing maintenance, especially for organizations lacking in-house expertise. Well-supported tools tend to ensure smoother adoption and better long-term results.
Customization and Flexibility
While some programs offer standardized workflows, others allow extensive customization to suit unique organizational needs. Consider your compliance scope—if your organization operates across multiple regions or industries, flexibility may be essential. Be mindful that highly customizable tools might require more time to configure and learn.
Cost and Long-Term Value
Budget considerations are critical, but the cheapest option isn’t always the best. Assess the total cost of ownership, including licensing, training, and support. Investing in a more comprehensive tool can pay off through increased efficiency and reduced risk, but only if it aligns with your organization’s size and complexity.
Frequently Asked Questions
How do I determine if an iso agent program is suitable for my organization’s size?
Assess your organization’s scale, complexity, and compliance maturity. Smaller organizations may benefit from simpler, more straightforward tools with guided workflows, while larger enterprises might require flexible, customizable solutions capable of handling multiple standards and locations. Many programs specify their target organization size or industry focus, so match these recommendations with your needs to find the best fit.
What level of automation should I prioritize in an iso agent program?
Automation can save significant time, especially in documentation, audit preparation, and reporting. If your organization handles frequent audits or complex documentation, prioritize programs with AI or automation features. However, if your team prefers more manual control or has limited budgets, a less automated but more affordable tool might be preferable. Balance automation with usability to avoid overwhelming your team.
Are there any common pitfalls when choosing an iso agent program?
One common mistake is prioritizing features without considering ease of use or support. Overly complex tools might lead to frustration and underutilization. Conversely, choosing a too-simple program can result in gaps in compliance coverage. Also, neglecting scalability—failing to consider future growth—can make a platform obsolete quickly. Carefully evaluate your current and anticipated needs before making a decision.
How important is ongoing support and training in these programs?
Ongoing support and training are vital, especially if your team is new to ISO standards. Reliable support reduces downtime during setup and helps resolve issues quickly. Training resources, such as tutorials, webinars, and user communities, empower your team to maximize the platform’s benefits. Consider programs that include comprehensive support options aligned with your internal expertise level.
Should I choose a program with more features or one that’s simpler to use?
Deciding between feature richness and simplicity depends on your organization’s needs. If you require extensive customization, complex reporting, or AI-driven automation, a more feature-heavy platform is appropriate. However, if your priority is quick implementation with minimal training, a simpler, more intuitive program will likely serve you better. Striking a balance between functionality and usability is key to long-term success.
Conclusion
For organizations seeking a comprehensive, hands-off approach, ISO 27001 Implementation Using AI offers advanced automation and speed, making it ideal for larger or more tech-savvy teams. Smaller or less experienced groups may find Building an ISMS with ISO/IEC 27001:2022 Made Practical more accessible due to its straightforward guidance. Budget-conscious buyers should consider tools that offer essential features without excessive complexity, while those with complex needs should prioritize customizable solutions. Ultimately, the right iso agent program depends on your organization’s size, expertise, and compliance goals.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.